A court in Antwerp, Belgium, issued a ruling on June 3, 2026, that banking law specialists have described as new, potentially influencing how financial institutions handle fraud reimbursements. The decision stemmed from a case involving an elderly couple who lost just under €50,000, equivalent to approximately R1 million. A fraudster, impersonating a bank employee, manipulated the couple into transferring the funds to an account located in Portugal. This key ruling on June 3, 2026, from the Antwerp court, has immediately drawn attention from legal and financial experts across the globe, who see its potential to reshape the landscape of victim compensation in an era of escalating financial cybercrime.
Belgian Precedent and Global Resonance
The National Financial Ombud Scheme (NFO) in South Africa reported a significant increase in fraud-related complaints, closing 3,651 cases in 2025 and recovering R442.9 million for consumers. This figure represents nearly double the number of complaints recorded in the preceding year, noting a growing crisis for consumers. Despite the rise in cases and recoveries, existing data indicates that rulings in 85% of banking fraud disputes favour the banks, suggesting a challenging environment for defrauded customers in South Africa. This stark statistic shows the uphill battle faced by victims seeking redress from financial institutions.
The recent Belgian ruling emerges as several countries consider or implement new frameworks for fraud reimbursement. The United Kingdom, for instance, became the first country to implement a mandatory Authorised Push Payment (APP) fraud reimbursement scheme in October 2024. This scheme requires payment institutions to compensate victims of APP fraud, which includes scams such as vishing and impersonation, for losses up to £85,000, equivalent to approximately R2 million. Reimbursement is mandated under the UK framework, with an exception only for cases where gross negligence on the part of the victim can be proven. This proactive approach in the UK sets a benchmark for other nations grappling with similar fraud challenges.
South African Fraud Landscape
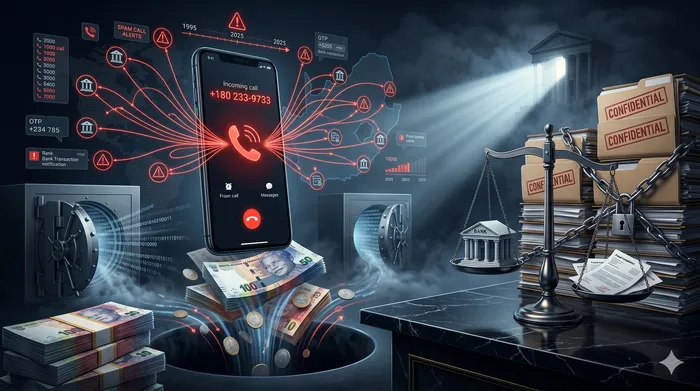
A case study submitted to IOL by financial fraud investigator Patrick Le Roux details a pattern of banking fraud familiar to victims across South Africa. A single telephone number, deceptively similar to a legitimate bank customer communications line with only one transposed digit in the final four numbers, was identified as a scam for 635 days before it was allegedly used to defraud Le Roux's elderly client in February 2025. This number’s long history of suspicious activity raises questions about the efficacy of current fraud detection and prevention mechanisms. During the 60 days preceding that incident, the number made 4,736 outbound calls and generated 376 spam reports on Truecaller, indicating a high volume of potentially fraudulent activity. The first documented victim linked to the same deceptive number filed a sworn affidavit with the South African Police Service in August 2023, nearly two years before Le Roux's client was targeted.
The fraud against Le Roux's client unfolded over more than three hours, with scammers employing authority, urgency, and sustained psychological pressure to coerce the victim into moving his own funds under the belief he was protecting them. This lengthy and sophisticated manipulation notes the psychological tactics employed by fraudsters. Le Roux stated, "This was not occasional fraud. It was industrial-scale impersonation." He further commented on the lack of consolidated data regarding such incidents, noting, "If every settlement is individually silenced, no regulator, no adjudicator, no future victim and no journalist has an accurate picture of how many times this number has been used and how many times the bank has paid." This lack of transparency, exacerbated by confidentiality clauses in settlements, obscures the true scale and nature of the problem.
Le Roux also argued that banks' reliance on one-time passwords (OTPs) as a defense in coercion cases is becoming unsustainable. "Those that continue to rely on ‘OTP delivered’ as a full defence in coercion cases will find that position increasingly difficult to sustain before regulators, adjudicators and the public," he said. This perspective challenges the banking sector's traditional stance on customer culpability when funds are transferred using authenticated credentials. Meanwhile, the Financial Sector Conduct Authority’s NPS 2030+ framework, intended to address such financial challenges, remains under development. The ongoing development of this framework shows the urgent need for full regulatory updates to tackle the evolving methods of financial fraud.
Expert Analysis and Legal Thresholds
Banks in Belgium, much like their counterparts in South Africa, frequently decline to reimburse victims of banking fraud, asserting that the victims themselves are grossly negligent for transferring funds. This common argument places the burden of responsibility squarely on the customer. South Africa currently lacks a mandatory framework for Authorised Push Payment (APP) fraud reimbursement, which contrasts with frameworks emerging in other nations. This absence leaves South African consumers more vulnerable compared to those in jurisdictions with stronger consumer protections. Financial institutions in South Africa also commonly include confidentiality clauses in fraud settlements, a practice that can obscure the full scope of such incidents. These clauses prevent public disclosure of the terms, potentially limiting transparency regarding the frequency and nature of fraud cases, and hindering a collective understanding of the problem.
Call for Systemic Change
The Antwerp court rejected the banks' logic, potentially establishing a precedent with significant global resonance regarding fraud reimbursements. This rejection of the gross negligence argument by the Belgian court is a critical development, challenging the prevailing narrative that victims are solely to blame. Geert Lenssens, a Belgian lawyer involved in the Antwerp case, estimates that true gross negligence, which is the legal threshold for denying reimbursement, applies in barely 1% of phishing cases. This assessment suggests that current banking practices regarding victim responsibility may not align with a strict interpretation of legal standards for negligence, and that banks may be overstating the extent of victim culpability. The ruling could therefore prompt a re-evaluation of how financial institutions assess culpability in fraud incidents, particularly in nations like South Africa that lack mandatory reimbursement frameworks. A shift in this assessment could lead to more equitable outcomes for victims and encourage banks to invest more in preventative measures rather than relying on victim blame. The implications of the Antwerp ruling extend beyond Belgium, offering a potential blueprint for other jurisdictions to reconsider their policies on APP fraud reimbursement and consumer protection.